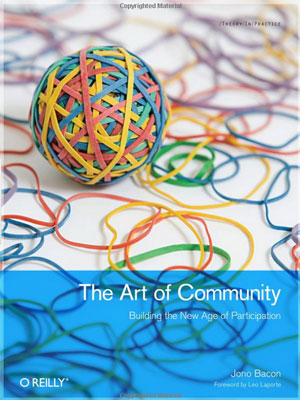
I’m Getting The Art of Community: Building the New Age of Participation Book by Jono Bacon

Art of Community

I’m getting “The Art of Community: Building the New Age of Participation“, a book written by Jono Bacon, Ubuntu Community Manager (UCM).

In this book, Jono offers a collection of experiences and observations from his involvement in building and managing communities, including his current position as Ubuntu Community Manager, arguably the largest community in open source software.

The content of the book, will help you to:

  • Develop a strategy, with specific objectives and goals, for building your community
  • Build simple, non-bureaucratic processes to help your community perform tasks, work together, and share successes
  • Provide tools and infrastructure that let contributors work quickly
  • Create buzz around your community to get more people involved
  • Track the community’s work so it can be optimized and simplified
  • Explore a capable, representative governance strategy for your community
  • Identify and manage conflict, including dealing with divisive personalities

This book is useful to those who are in a position that manages and responsible towards online communities, including day-to-day management, governance, managing conflics and how to promotes the community effectively.

An online preview is this book is available from Amazon Bookstore
“, a book written by Jono Bacon, Ubuntu Community Manager (UCM). website.

Limiting the number of connections to SSH Server using Iptables

This is the quickest way to limit the number of connection to your SSH server with iptables.

[bash]
sudo /sbin/iptables -A INPUT -p tcp –syn –dport 22 -m connlimit –connlimit-above 5 -j REJECT
[/bash]

This will only allow up to 5 concurrent connections to the SSH server, subsequent connections will be rejected by iptables, thus this can thwarts Brute-force attempts to your server.

More Articles About Securing SSH Server

How to Secure SSH server from Brute-Force and DDOS with Fail2ban ( Ubuntu )

Fail2ban is a security tool used for preventing brute-force attack and Distributed Denial of Service (DDoS) attack to your GNU/Linux box.

Fail2ban monitors failed login attempts and subsequently blocks the ip address from further logins. Although Fail2ban can also be used to secure other services in Ubuntu server, in this post, I will only focus on securing SSH server.

Step 1: Install Fail2ban and (optionally) sendmail

sudo apt-get install fail2ban
sudo apt-get install sendmail-bin

Step 2: Setting up Fail2ban

Next, you need to configure fail2ban by creating a copy of ‘jail.conf’ to ‘jail.local’

cd /etc/fail2ban
sudo cp jail.conf jail.local

Step 3: General fail2ban configuration

Edit fail2ban configuration file using your favorite text-edito (I personally use ‘nano’)

sudo nano /etc/jail.local

You can set IP address for fail2ban to ignore, IP addresses can be separated by space.

Bantime is the duration of time that you want fail2ban to block suspicious attempt, the value is in seconds
Maxretry is the number of failed attempts before fail2ban block the IP-address, in this case 3600 means 1-hour ban

# "ignoreip" can be an IP address, a CIDR mask or a DNS host
ignoreip = 127.0.0.1 192.168.1.1
bantime  = 3600
maxretry = 3 

Step 4: Enabling ssh and ssh-ddos protection
Find ssh configuration under [ssh] heading, and enable it.

[ssh]
enabled = true
port    = ssh
filter  = sshd
logpath  = /var/log/auth.log
maxretry = 3 

Similarly, you can also enable [ssh-dos] protection by changing the enabled value to “enabled = true”

[ssh-ddos]
enabled = true
port    = ssh
filter  = sshd-ddos
logpath  = /var/log/auth.log
maxretry = 2

Step 5: Enable Sending Notification Email (optional)
Optionally you can have fail2ban sends you notification email in case of suspicious login detected. To do that, you need to locate destemail settings and changed it to your email

destemail = security@mypapit.net

Fail2ban can use ‘sendmail’ and ‘mail’ application to send notification email

Step 6: (Re-)start Fail2ban
After all is done, you may save the file, and (re)start the fail2ban service

sudo /etc/init.d/fail2ban restart

You can test the configuration by trying to login into your box. You may also check fail2ban log in /var/logs/auth.log (or in other directory specified in jail.local)

For more information about fail2ban, you can read : the official fail2ban manual

Recommended Reading

Dell Inspiron Duo Tablet Notebook Running Ubuntu (with Ubermix)

The video shows how cool Dell Inspiron Duo is when running Ubuntu.

This particular demo uses Ubuntu 10.10 (Maverick Meerkat) with Ubermix customization, which contains a collection of application suitable for netbook users.

Ubermix can be downloaded from its official website, please check the Netbook/table model specific instructions for proper installations.

Supported Netbooks

  • Dell Inspiron DUO iD-4495FNT Laptop
  • ASUS EEEPC 900 BK090XNetbooks)
  • ASUS Eee PC 1015PX
  • Dell Inspiron Mini 1018
  •  

    Ubuntu One Files client for Android phones

    Ubuntu One Files for Android is an application written by Micha? Karnicki as part of Google Summer of Code Project (GSoC) 2010. The client is licensed under the GNU Affero GPL v3 and its source code is available from Launchpad.

    Google Android Ubuntu One files

    The application lets you synchronize your phone contacts, files and photo gallery on the cloud automatically. Ubuntu One files also offers convenient feature to change the visibility of your files, making it easier for you to share files with the rest of the world.

    Ubuntu One Files is also available on the Android Market, free of charge.

    Note: Ubuntu One is a service similar to Box.net that enables you to store your files on the cloud. You do not need to be an Ubuntu user to use Ubuntu One. Each registered user are given 2GB space for free.