Some services require you to generate random hex numbers to be used as a password or random auth token for authentication. The simplest method is to use this openssl cli command
openssl rand -hex 24
Free and Open Source blogger with an attitude
Some services require you to generate random hex numbers to be used as a password or random auth token for authentication. The simplest method is to use this openssl cli command
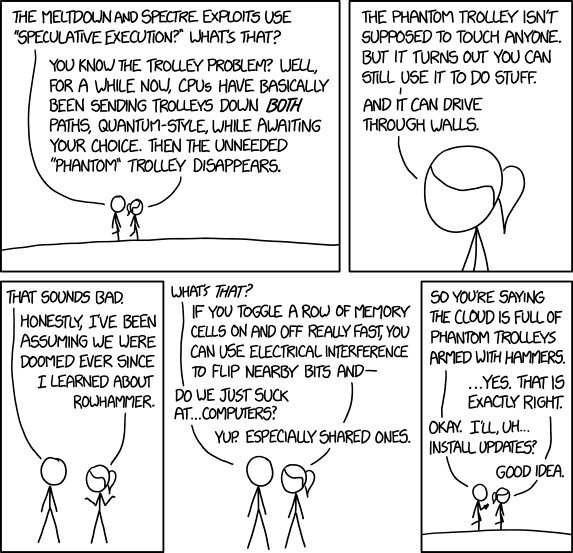
openssl rand -hex 24This XKCD strip explains what essentially Meltdown vulnerability which affects Intel microprocessor
LLGAL (llgal) is an tool which can automatically generate gallery on your website. llgal is handy if you want to generate photo album out of photos organized in directories/folders.
Running llgal from the console is easy as typing the llgal command at the root directory of your photos.
llgal --exif --li -L -R --title "Album Name" --sx 960 --sy 720 --tx 250 --ty 150
In Ubuntu, the gallery’s theme is located in “/usr/share/llgal/” directory and my customized theme which supports mobile phone can be downloaded here: llgal.zip (mobile enabled)
Personally, i use llgal to generate cctv tiles automatically on my Ubuntu server from which my TP-LINK NC450 and NC250 IP camera uploads through its FTP functions when it detects movements/motion.
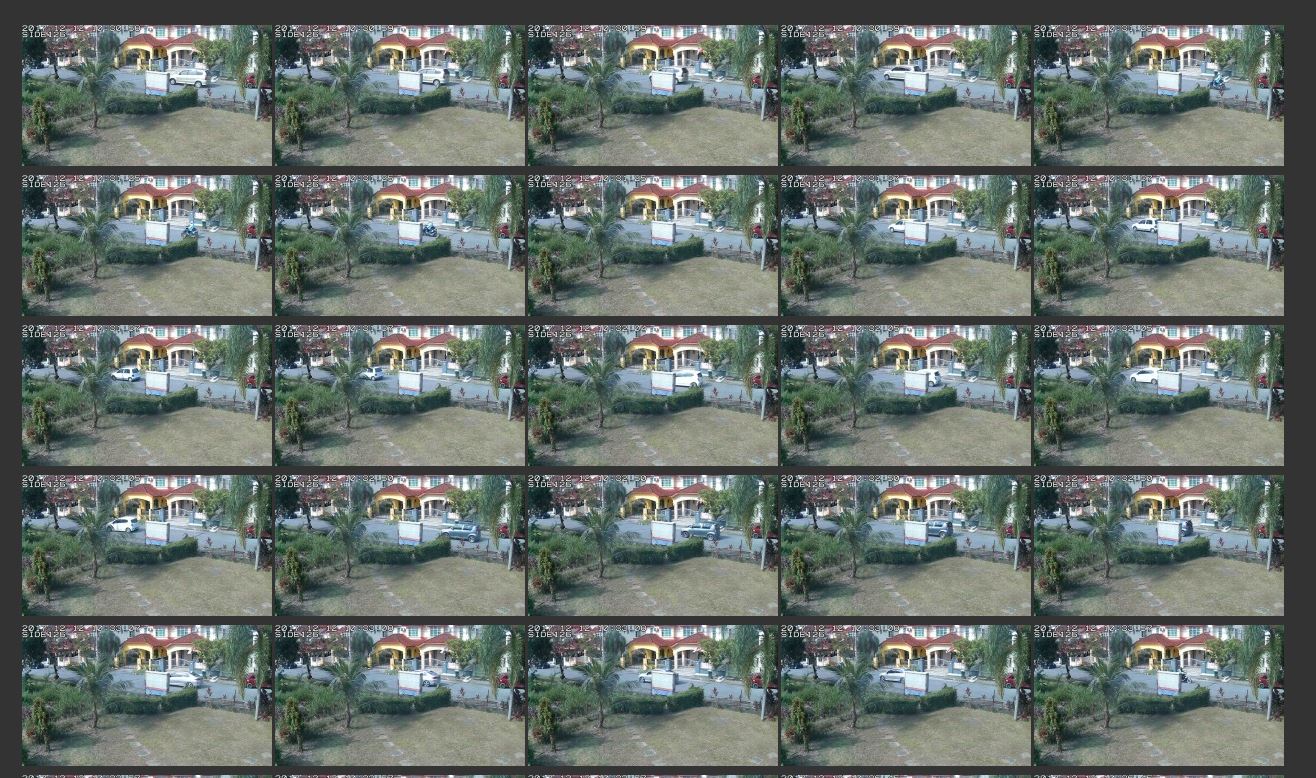
llgal can be installed on Ubuntu by running this command
apt -y install llgal
Alternatively you can compile and install llgal directly from its repository
https://github.com/bgoglin/llgal
Cracking zip password can be made easy with cracker-ng
Installation is simple, assuming you use Debian, Ubuntu or any other similar operating system :
$ git clone https://github.com/BoboTiG/cracker-ng.git
$ cd cracker-ng

# For testers and contributors, always work with on the devel branch:
$ git checkout devel

$ make
Cracking is relatively simple, assuming you have downloaded the awesome Crackstation’s wordlist dictionary.
$ zipcracker-ng -f targetfile.zip -w crackstation-human-only.txt
Additionally zipcracker-ng can also be used with other brute-forcing cracking tool such as john and
$ john --incremental --stdout | zipcracker-ng -f FILE -

$ crunch 1 8 -f charset.lst lalpha | zipcracker-ng -f FILE -
Crackstation wordlist is one of the most (if not the most) comprehensive wordlist which can be used for the purpose of dictionary -attack on passwords.
The wordlist comes in two flavors:
Personally, I’ve already downloaded the full wordlist via torrent, and tested it against few PDF files (using pdfcrack) and UNIX password cracking (using John), all my test cases were successful. In my opinion, the wordlist is comprehensive for my need.
Since it looked like it took a significant effort to compile this wordlist, I rather advocate those who are interested to donate/buy the wordlist from: https://crackstation.net/buy-crackstation-wordlist-password-cracking-dictionary.htm
I’ve come across an PDF which was sent to my email from an automated banking system. Unfortunately, the PDF file is encrypted and I’ve no way of knowing the password (or actually I’ve forgotten the password).
Fortunately, my Ubuntu box comes with application which allows me to crack the PDF file within a reasonable time.
You need to install pdfcrack to crack pdf file. In Ubuntu/Debian system, you simply need to run
sudo apt-get -y install pdfcrack
Then for actual cracking, you can run
pdfcrack -n5 -m10 encrypted.pdf
Where -n [minimum length] to brute-force, and -m [maximum length] to brute-force.
pdfcrack can also accept a file input containing list of words (dictionary attack). For dictionary-attack just run
pdfcrack --wordlist=dictionary.txt encrypted.pdf