How to Hide OpenSSH Ubuntu version from Nmap and other scanners

In Ubuntu or Debian, a default OpenSSH server will display OpenSSH version alongside with Ubuntu/Debian distribution banner:

$ telnet repeater.my 172.16.91.20 22 
Trying 172.16.91.20...
Connected to 172.16.91.20.
Escape character is '^]'.
SSH-2.0-OpenSSH_6.6.1p1 Ubuntu-2ubuntu2

You can hide the identifying part of Ubuntu-2ubuntu2 from the server banner by editing /etc/ssh/sshd_config file, and adding “DebianBanner no” either at the end of the file, or just under “Port 22” configuration in “/etc/ssh/sshd_config

#/etc/ssh/sshd_config 
# What ports, IPs and protocols we listen for

Port 22
DebianBanner no

Save and restart OpenSSH server by typing

sudo service ssh restart

Now the response will just be:

Trying 172.16.91.20...
Connected to 172.16.91.20.
Escape character is '^]'.
SSH-2.0-OpenSSH_6.6.1p1

Happy trying!

Further Reading: Ubuntu Server Administrator Reference

Install NGINX with PageSpeed using *.deb for Ubuntu LTS (AMD64)

Hello there, I’ve made an easily installable *.deb NGINX package with PageSpeed. The package is made for Ubuntu LTS on AMD64 machine.

Ubuntu 14.04 LTS – nginx 1.8.0 with PageSpeed

  1. nginx-full_1.8.0-1+trusty1-mypapitubuntu4_amd64.deb Full package
  2. nginx-extras_1.8.0-1+trusty1-mypapitubuntu4_amd64.deb Extra package

Ubuntu 14.04 LTS – nginx 1.8.0 with PageSpeed: Other Package

  1. nginx-common_1.8.0-1+trusty1-mypapitubuntu4_all.deb
  2. nginx_1.8.0-1+trusty1-mypapitubuntu4_all.deb
  3. nginx-doc_1.8.0-1+trusty1-mypapitubuntu4_all.deb

Installing nginx-extras or nginx-full is as easy as running this command

sudo dpkg -i nginx-common_1.8.0-1+trusty1-mypapitubuntu4_all.deb
sudo dpkg -i nginx-full_1.8.0-1+trusty1-mypapitubuntu4_amd64.deb
sudo dpkg -i nginx_1.8.0-1+trusty1-mypapitubuntu4_all.deb

Attention : Once installed, the PageSpeed configuration file can be found in “/etc/nginx/conf.d/pagespeed.conf”

Verify Installation
To verify whether nginx with pagespeed has been installed, type

nginx -V

Verify Installation with a preinstalled nginx
If you’ve another version of nginx installed on your system, take note that the nginx-pagespeed from *.deb is installed in “/usr/local/bin”

/usr/local/bin/nginx -V

It will output something like this:

nginx version: nginx/1.8.0
built with OpenSSL 1.0.1f 6 Jan 2014
TLS SNI support enabled
configure arguments: --with-cc-opt='-g -O2 -fPIE -fstack-protector --param=ssp-buffer-size=4 -Wformat -Werror=format-security -D_FORTIFY_SOURCE=2' --with-ld-opt='-Wl,-Bsymbolic-functions -fPIE -pie -Wl,-z,relro -Wl,-z,now' --prefix=/usr/share/nginx --conf-path=/etc/nginx/nginx.conf --http-log-path=/var/log/nginx/access.log --error-log-path=/var/log/nginx/error.log --lock-path=/var/lock/nginx.lock --pid-path=/run/nginx.pid --http-client-body-temp-path=/var/lib/nginx/body --http-fastcgi-temp-path=/var/lib/nginx/fastcgi --http-proxy-temp-path=/var/lib/nginx/proxy --http-scgi-temp-path=/var/lib/nginx/scgi --http-uwsgi-temp-path=/var/lib/nginx/uwsgi --with-debug --with-pcre-jit --with-ipv6 --with-http_ssl_module --with-http_stub_status_module --with-http_realip_module --with-http_auth_request_module --with-http_addition_module --with-http_dav_module --with-http_geoip_module --with-http_gunzip_module --with-http_gzip_static_module --with-http_image_filter_module --with-http_spdy_module --with-http_sub_module --with-http_xslt_module --with-mail --with-mail_ssl_module --add-module=/home/mypapit/source/nginx-1.8.0-1+trusty1/debian/modules/nginx-auth-pam --add-module=/home/mypapit/source/nginx-1.8.0-1+trusty1/debian/modules/nginx-dav-ext-module --add-module=/home/mypapit/source/nginx-1.8.0-1+trusty1/debian/modules/nginx-echo --add-module=/home/mypapit/source/nginx-1.8.0-1+trusty1/debian/modules/nginx-upstream-fair --add-module=/home/mypapit/source/nginx-1.8.0-1+trusty1/debian/modules/ngx_http_substitutions_filter_module --add-module=/home/mypapit/source/nginx-1.8.0-1+trusty1/debian/modules/ngx_pagespeed-release-1.9.32.4-beta

Take note at the bolded text to verify whether pagespeed module has been installed.
An easy way to Install OpenVPN in CentOS – snippet

Source: https://zulfah.my/files/openvpnsetup/vpn_install.txt

Got this while surfing the internet. A no brainer way to install and setup OpenVPN in CentOS. The only thing left is to open port 1194/udp 1337/udp from firewall / router

yum update -y && yum -y install nano unzip wget gcc make rpm-build autoconf.noarch zlib-devel pam-devel openssl-devel

cd /home

wget http://dl.fedoraproject.org/pub/epel/6/i386/epel-release-6-8.noarch.rpm && rpm -Uvh epel-release-6-8.noarch.rpm

yum update -y && yum -y install openvpn

cd /etc/openvpn

wget https://zulfah.my/files/openvpnsetup/configuration-OpenVPN/server.conf.txt

wget https://zulfah.my/files/openvpnsetup/configuration-OpenVPN/easy-rsa-2.2.0_master.tar.gz

mv server.conf.txt server.conf

tar -zxvf easy-rsa-2.2.0_master.tar.gz

cd /etc/openvpn/easy-rsa-2.2.0_master/easy-rsa/2.0

rm -rf vars

rm -rf openssl-1.0.0.cnf

wget https://zulfah.my/files/openvpnsetup/configuration-OpenVPN/easyrsa/vars

wget https://zulfah.my/files/openvpnsetup/configuration-OpenVPN/easyrsa/openssl-1.0.0.cnf

chmod 755 *

source ./vars

./vars

./clean-all

./build-ca
*change hostname

./build-key-server server
*change hostname

./build-dh

cd /etc/openvpn/easy-rsa-2.2.0_master/easy-rsa/2.0/keys

cp dh1024.pem ca.crt server.crt server.key /etc/openvpn

iptables -t nat -A POSTROUTING -s 10.8.0.0/24 -o eth0 -j MASQUERADE

service iptables save

nano -w /etc/sysctl.conf
*change net.ipv4.ip_forward = 1

sysctl -p

echo 0 > /selinux/enforce

cd /etc/openvpn

wget https://zulfah.my/files/openvpnsetup/configuration-OpenVPN/openvpn-auth-pam.zip

unzip openvpn-auth-pam.zip

service openvpn start

chkconfig openvpn on

useradd testuser -d /dev/null

passwd testuser


Python code: List most popular URL from Apache/NGINX ‘access.log’ file

Found a great Python code snippet for listing the most popular URL from Apache / NGINX ‘access.log’ file. Very practical!

import collections

logfile = open("access.log", "r")

clean_log=[]

for line in logfile:
    try:
        # copy the URLS to an empty list.
        # We get the part between GET and HTTP
        clean_log.append(line[line.index("GET")+4:line.index("HTTP")])
    except:
        pass

counter = collections.Counter(clean_log)

# get the Top 50 most popular URLs
for count in counter.most_common(50):
    print(str(count[1]) + "\t" + str(count[0]))

logfile.close()

The code is very handy if you want to find out the most popular URL or pages in your website, crucial information for optimization, IMHO.

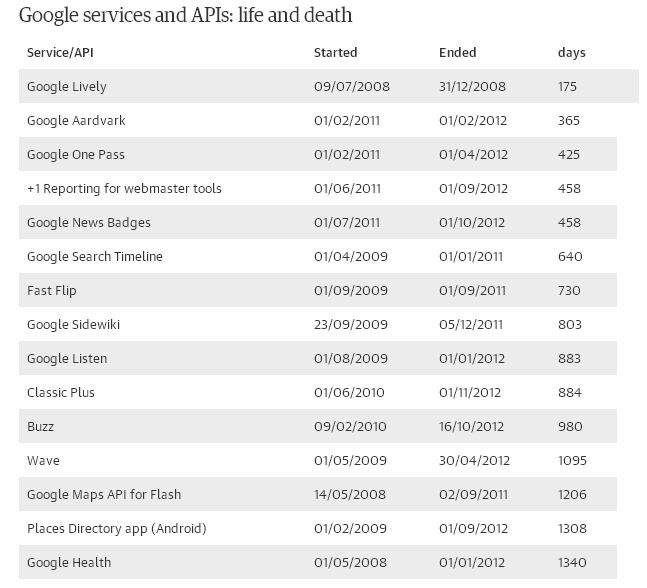
Using a new Google API or Service? It might not last long…

I read an interesting analysis on the lifespan of some of the Google service and API that has been cancelled: http://www.theguardian.com/technology/2013/mar/22/google-keep-services-closed

Based on the analysis at the time of the writing, Google service has a mean lifespan of 1,459 days.

An interesting point to ponder, especially if your applications/services depends on one or more Google services.

Screenshot below:
google-service

What ever happened to 1Malaysia Email – Tricubes, Pemandu, anyone??

What ever happened to 1Malaysia email, a project that said to be valued at 5.3 milions (MAVcap funding) ?

Source: