Download Wordlist for dictionary attack

Crackstation wordlist is one of the most (if not the most) comprehensive wordlist which can be used for the purpose of dictionary -attack on passwords.

The wordlist comes in two flavors:

  1. Full wordlist (GZIP-compressed (level 9). 4.2 GiB compressed. 15 GiB uncompressed)
  2. Human-password only wordlist (GZIP-compressed. 247 MiB compressed. 684 MiB uncompressed)

Personally, I’ve already downloaded the full wordlist via torrent, and tested it against few PDF files (using pdfcrack) and UNIX password cracking (using John), all my test cases were successful. In my opinion, the wordlist is comprehensive for my need.

Since it looked like it took a significant effort to compile this wordlist, I rather advocate those who are interested to donate/buy the wordlist from: https://crackstation.net/buy-crackstation-wordlist-password-cracking-dictionary.htm

Cracking PDF file with PDFCrack in Linux

I’ve come across an PDF which was sent to my email from an automated banking system. Unfortunately, the PDF file is encrypted and I’ve no way of knowing the password (or actually I’ve forgotten the password).

Fortunately, my Ubuntu box comes with application which allows me to crack the PDF file within a reasonable time.

Using ‘pdfcrack’ to crack PDF file

You need to install pdfcrack to crack pdf file. In Ubuntu/Debian system, you simply need to run

sudo apt-get -y install pdfcrack

Then for actual cracking, you can run

pdfcrack -n5 -m10 encrypted.pdf

Where -n [minimum length] to brute-force, and -m [maximum length] to brute-force.

pdfcrack can also accept a file input containing list of words (dictionary attack). For dictionary-attack just run

pdfcrack --wordlist=dictionary.txt encrypted.pdf

Securing SSH port and limiting IP address connection with Firewall in Ubuntu

UFW: Securing SSH
UFW or Uncomplicated Firewall is a firewall package in Ubuntu. UFW can be used to secure SSH ports in Ubuntu server.

In order to secure OpenSSH, we must first disable UFW and allow all SSH rule.

sudo ufw disable
sudo ufw delete allow ssh

Then we add IP Address to be allowed to connect to SSH port. In this case I assume that “192.168.1.10” would be allowed to be connected to the server. You can replace IP Address, with any IP Address that you prefer.

sudo ufw allow from 192.168.1.10 to any port ssh

You can also add other IP Address that can be connected to SSH port. In this case, I chose em>”172.25.100.1″.

sudo ufw allow from 172.25.100.1 to any port ssh

Alternatively, you could also specify port number and protocol

sudo ufw allow from 192.168.1.10 to any port 22 proto tcp

Only allow SSH connections from certain subnets

sudo ufw allow from 192.168.1.0/24 to any port 22 proto tcp

Note: Adding firewall rules to only allow SSH connection from certain subnets would increase the server security, further reducing brute-force attack.

Further Reading: Ubuntu Server Administrator Reference

Solving “Connection is encrypted using obsolete cipher suite” warning from Chrome

Here is a how to on how to solve the dreaded warning “Your connection is encrypted using obsolete cipher suit” from Google Chrome.

Firstly the warning had nothing to do with using cheap or self-signed TLS/SSL security certificate, but it has to do with cipher suite used on the server part.
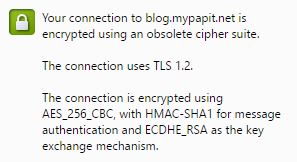
obsolete-cipher-suite

So if you are a system administrator, you can edit the site config to include a more modern cipher.

NGINX Server

Using nginx, add the line containing “ssl_cipers” to the site config.

# /etc/nginx/sites-enable/example.conf 
server {
 listen 443 ssl;
 root /var/www/example.com/;
 server_name example.com;
   ssl_ciphers 'ECDHE-RSA-AES128-GCM-SHA256:ECDHE-ECDSA-AES128-GCM-SHA256:ECDHE-RSA-AES256-GCM-SHA384:ECDHE-ECDSA-AES256-GCM-SHA384:DHE-RSA-AES128-GCM-SHA256:DHE-DSS-AES128-GCM-SHA256:kEDH+AESGCM:ECDHE-RSA-AES128-SHA256:ECDHE-ECDSA-AES128-SHA256:ECDHE-RSA-AES128-SHA:ECDHE-ECDSA-AES128-SHA:ECDHE-RSA-AES256-SHA384:ECDHE-ECDSA-AES256-SHA384:ECDHE-RSA-AES256-SHA:ECDHE-ECDSA-AES256-SHA:DHE-RSA-AES128-SHA256:DHE-RSA-AES128-SHA:DHE-DSS-AES128-SHA256:DHE-RSA-AES256-SHA256:DHE-DSS-AES256-SHA:DHE-RSA-AES256-SHA';

        ssl_protocols TLSv1.1 TLSv1.2;
        ssl_prefer_server_ciphers on;
...
...
...

}

sudo service nginx restart

Apache HTTP Server

For those who are using Apache HTTP server, you can edit the VirtualHost file from “/etc/apache2/sites-enable/” directory.

<VirtualHost *:443>
    ...
    SSLEngine on
    SSLCertificateFile      /path/to/signed_certificate
    SSLCertificateChainFile /path/to/intermediate_certificate
    SSLCertificateKeyFile   /path/to/private/key
    SSLCACertificateFile    /path/to/all_ca_certs

    # Intermediate configuration, tweak to your needs
    SSLProtocol             all -SSLv2 -SSLv3
    SSLCipherSuite          ECDHE-RSA-AES128-GCM-SHA256:ECDHE-ECDSA-AES128-GCM-SHA256:ECDHE-RSA-AES256-GCM-SHA384:ECDHE-ECDSA-AES256-GCM-SHA384:DHE-RSA-AES128-GCM-SHA256:DHE-DSS-AES128-GCM-SHA256:kEDH+AESGCM:ECDHE-RSA-AES128-SHA256:ECDHE-ECDSA-AES128-SHA256:ECDHE-RSA-AES128-SHA:ECDHE-ECDSA-AES128-SHA:ECDHE-RSA-AES256-SHA384:ECDHE-ECDSA-AES256-SHA384:ECDHE-RSA-AES256-SHA:ECDHE-ECDSA-AES256-SHA:DHE-RSA-AES128-SHA256:DHE-RSA-AES128-SHA:DHE-DSS-AES128-SHA256:DHE-RSA-AES256-SHA256:DHE-DSS-AES256-SHA:DHE-RSA-AES256-SHA
    SSLHonorCipherOrder     on
    SSLCompression          off

    # OCSP Stapling, only in httpd 2.3.3 and later
    SSLUseStapling          on
    SSLStaplingResponderTimeout 5
    SSLStaplingReturnResponderErrors off
    # On Apache 2.4+, SSLStaplingCache must be set *outside* of the VirtualHost
    SSLStaplingCache        shmcb:/var/run/ocsp(128000)
 
    # Enable this if your want HSTS (recommended)
    # Header add Strict-Transport-Security "max-age=15768000"
 
    ...
</VirtualHost>

You can restart Apache HTTP server by running

sudo service apache2 restart
My GPG Public Key (mypapit)

Since there are some people out there who asked about my gpg public key, now I decided to published them on my web.

Feel free to send me messages or files using my public-key.

KeyID: 0AFAD5F8 
Mohammad Hafiz bin Ismail (mypapit) 

-FYI – mypapit@gmail.com

You can get my GPG Public key here…


-----BEGIN PGP PUBLIC KEY BLOCK-----
Version: GnuPG v1

mQENBFXRsKwBCACgd/WbmC8UgCUeLwim12tMt8Y2bjCb/dlSamPB9XiRgYMqdxWQ
IRyaZ1YzDOvfzgd3qmHztOZ3YxksD1isvT0Uo/29atAz8h1FVt4MQdEFpgk+WGQO
P25UfZB+g9EP6jFIVl5U7gJ4vRknZh+sBdeBAYGwc6JwnP6SouKoJKhTfJyeqgIy
qlNwnIXrShRbUofUkyjzTPIvv7d6ZPiw6ITyaj0YJN9Qr1ddTldDsBGP2dhEaWot
CdG62TAmW2b+31gxnEE/tD4t12hzqZoBq/5j6OfS219p9RYzIBnAWKa1/jw2gixV
2hglwsn+3QU7ROc+yp8ML60xyQsWankDwuSVABEBAAG0N01vaGFtbWFkIEhhZml6
IGJpbiBJc21haWwgKG15cGFwaXQpIDxteXBhcGl0QGdtYWlsLmNvbT6JATgEEwEC
ACIFAlXRsKwCGwMGCwkIBwMCBhUIAgkKCwQWAgMBAh4BAheAAAoJEPJRNDIK+tX4
c1MH/2MFnSBBZfWIEB5t8y8AWTYH+q/Zg1r6y3Hb58kmExNvC2lbo8KgH5jXE7FL
nyWudftbAlHIMsswQroVriqa3cUjVnqTeY9BI2gNFvCjXAlNH9zcYhOO96aoRdIX
o4A5JjFw4QCWRLIL1K7TJ2vC1yf0pMLt3kIqgX1Mn+tddhpB3y4vFzO2YjGIwOi1
4qDUdCiMu7R/e3G/jM/GKU6Dt2CZaNzpxh8XGYp5v27BO3NS6dMsPJaz/8CyX4kd
xdnqnXQkdQ34DsBEM/CcsjxszKP0nzL+RXSXlvwfpK456APfaBumIUfletSkM6k7
smQVDjrCRRD5jlyMvgRALpU+Xsi5AQ0EVdGwrAEIANaQguSr42PU4UatNCfnU0Ve
udW/bJaADqdrTIipn+pIqqpeOLKxOyeGbi/THosdsRZbXyfLwHmZm4R6E7yXtJka
2wFdSqubWqsr92sSVV+K/YT/KjYFEd+n6aPrEtvRrwZK9df5a8GEhwkW/GS7/ZbD
6PakV8/4S4OywjtoDOP9V9lRf6lbmAyj3cLapcpkZbWK4NRYE7w9b7n8aNwCjblO
1vYs13gLrU0AAzZUehxrY5Nn+vduEQDcyg7BakJFzdQzsh1akXwSdL9Fhy/L5YSA
7jcZ7pfRdXuWqkeOWM/Cmd6K7+2qIlQX2g1cjvGUGigNaPnnylD8IihOqQcnG0cA
EQEAAYkBHwQYAQIACQUCVdGwrAIbDAAKCRDyUTQyCvrV+CbsB/9KKsLpmP1blyKI
CnND5IBg6HcCX+OpMcxlMD+UiJXeZ7k9IOqZ4hW0A+GcKK/SPBx4VaDseMiuzEHk
ki2l+YiSFupvb+9/PrsdBxc+qabkO+QJrlyDn0mcSuChgt1EJhsx6TZx//Mowm3n
9jqiglvUVIH8AllsQqlVPD/JOCd6uPWilnwnXEiBj0CteOka1filECe5xOnPkBw9
chpgAuOgRa+fhhjR48wV5uNgKUTo1KjT/aKEpeDRVVZXh5AXmKYzZ1wxwJrBbIK2
uLVvheCufc4YyORigQ5rIio/J7IqzCy8CqbRV/ca79WCw5d4wEeGHeocNI4H4VOe
Pk5z3DKO
=gAgL
-----END PGP PUBLIC KEY BLOCK-----

Text link: Mypapit GPG Public Key