Linux Package Manager Cheat Sheet Reference Chart

Linux comes in many flavors or distros, and each distro handles software installation differently from one another. Most GNU/Linux distro uses a package management system to manage software updates/instalation/removal in order to help users administer their Linux systems.

However, many of these package management system has different interface and commands, as such users from Ubuntu (or Debian based) might only be familiar with ‘apt’ or dpkg while Fedora (Red Hat based) users might only familiar with yum and rpm, which may create confusion when users from either distro were to exchange environments.

Luckily, somebody was kind enough to provide these users with Linux Package Manager Cheat Sheet which act as a reference point whenever a user had to switch to another distro which uses package management that are not familiar with them.
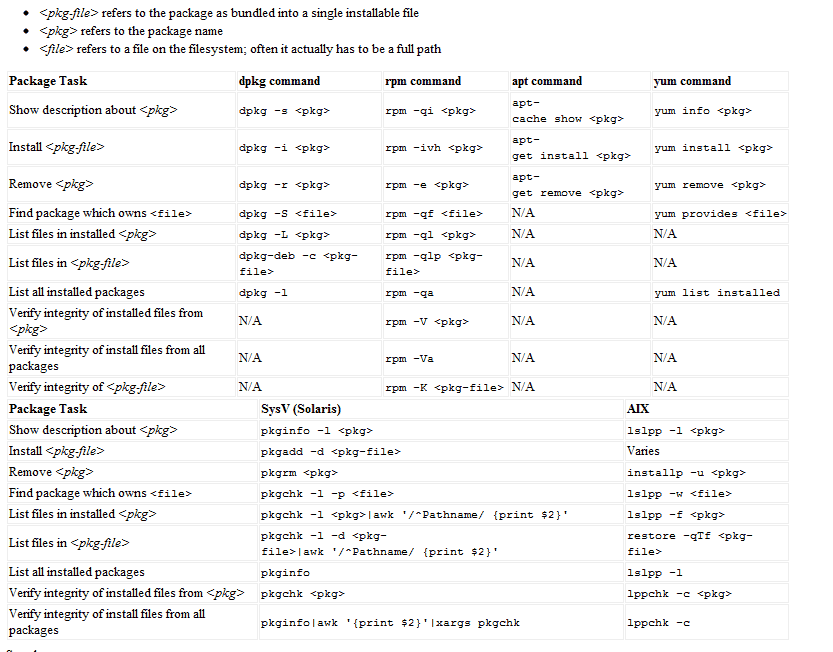
The package management software listed are for: apt,dpkg,yum, rpm, pkg* (slackware based) and AIX-based lsl**.

[ Source ]

How to secure server from SYN-flood attack using iptables

SYN-flood attack is commonly utilized as a mean to disrupt network communication and it is a form of (Distributed Denial-of-Service) DDOS attack. RFC4987 details common mitigation to deal with SYN-flood attack.

However in this post, I’m going to share you the method that I use to reduce the risk of SYN-flood attack from my department computers, with iptables
[bash]
/sbin/iptables -N syn-flood
/sbin/iptables -A syn-flood -m limit –limit 100/second –limit-burst 100 -j RETURN
/sbin/iptables -A syn-flood -j LOG –log-prefix "SYN-flood attempt: "
/sbin/iptables -A syn-flood -j DROP
[/bash]

RFC4987 suggests the use of SYN-cookie for added protection. You can enable SYN-cookie protection in Linux by running this command (as root):
[bash]
echo 1 > /proc/sys/net/ipv4/tcp_syncookies
[/bash]

hope that helps…

Note: I’m not a full-time sysadmin as I’ve a different dayjob, but I was put incharged in securing part of my school’s computer network, so there.

Please update/patch and secure Litespeed web server

Due to the widespread of Litespeed 0-day attack which has affected local websites, it’s imperative for all sysadmin and website operator to patch/update and upgrade the security of the Litespeed web server.

This attack is dangerous particularly because the attacker can gain shell access with the same privileges of the web server or the user that runs the web server. Usually this allow the attacker to peek into database content and downloads it.

Patch now!, the security and privacy of your users are at the stake!

How to Hide Apache2 and PHP version without using mod_security in Ubuntu Linux

Although security by obscurity is not the best policy to protect your IS assets, but it is still useful to thwarts simple network scanner or newbie crackers.

Note: This tip is written for Ubuntu Linux, the steps is similar to other GNU/Linux distro, albeit with a slight variant.

Hiding Apache2 version
Edit /etc/apache2/apache2.conf

Add these lines at the end of the file:
ServerSignature Off
ServerTokens Prod

Restart Apache2
[bash]
sudo /etc/init.d/apache2 restart
[/bash]

Hiding PHP version
Edit /etc/php5/apache2/php.ini file

Find these lines, and switch it off:
expose_php = Off
display_errors = Off

Additionally you may disable certain ‘risky’ functions in php by editing the disable_functions line:
disable_functions = phpinfo, system,show_source,

Finally, you may restart Apache2 web server.
[bash]
sudo /etc/init.d/apache2 restart
[/bash]

3 Reasons Behind why I Hate CPanel Web Hosting

Adding Subdomain / Domain creates a subdirectory
Adding Subdomain, and add-on Domain is a pain-in-the-ass as it creates a subdirectory in the root web directory, meaning that any web-users can abuse this by adding trailing subdirectory ‘subdomain’ http://yourdomain.com/subdomain/ to access http://subdomain.yourdomain.com/

Outdated Pre-package Software
Cpanel came with outdated pre-packaged software, PHP, MySQL and PostgreSQL and other libraries that is outdated compared to the one available on the host operating system. The problem is not about how outdated the software packages are, but the how often these package are being patched. CPanel vendor very notorious for not providing timely patches which would compromise the security of the web application.

Can’t change DNS setting easily from the panel
Unlike DirectAdmin, CPanel does not offer an easy way to change DNS record of domain easily as the option is not offered by default to the control panel. Although this can be mitigated by having your domain points to a 3rd party NS, it’s still one of the thing that gets me down with CPanel.

My Thoughts
CPanel is an excellent control panel for beginner as it offers a lot of options and functionality with a simple user-interface. However, personally, I prefer to use other control panel such as DirectAdmin or Plesk for my web hosting use.

p/s: Currently I’m on VPS without standard control panel.