Simple SSH Tunnelling tips

SSH tunelling is usually used to avoid firewall restriction or to ensure point-to-point encrypted communication.

For example, if you want to send email to smtp server “smtp.yourserver.com” on port 587, but your organization currently blocking smtp port 25 and 587, then you can benefit from SSH tunelling to avoid from being blocked.

To get around that, you need an intermediate server, fastssh.com currently provide SSH tunneling service with 7days trial account.

Simple SSH tunnelling command, if you’re using fastssh.com service.

ssh -f fastssh.com-username@sg.fastssh.com -L 2000:smtp.yourserver.com:587 -N

So in your mail setting, you can safely put, SMTP Server = “127.0.0.1”, SMTP port = “2000” in your setting, in order to automagically connect to “smtp.yourserver.com” port 587 without firewall restriction.

Please refer here, for port forwarding in Microsoft Windows environment using PuTTY
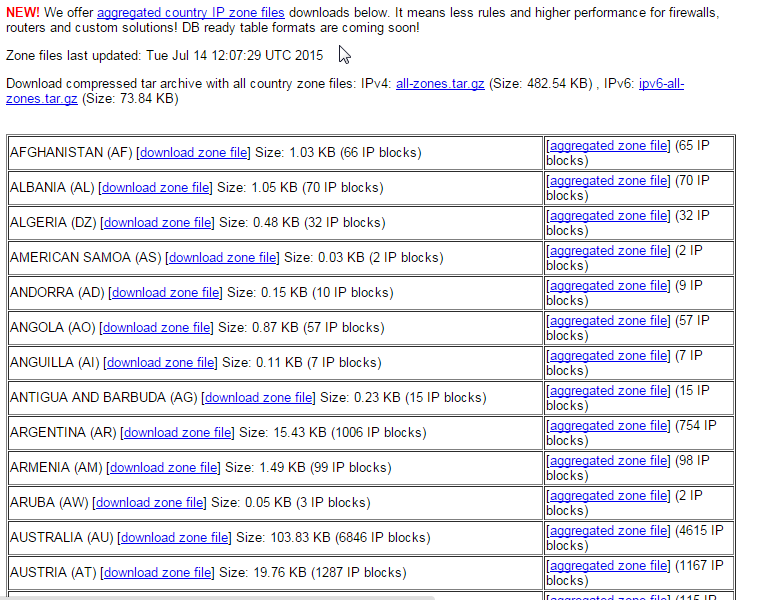
IPdeny.com – Download collections of Country IP Addresses

IPdeny.com is a service which offers a free collection of Regional and Country IP address blocks list.

ipdeny

The IP address blocks is useful for application developer and system administrator to enhance their system. For example, application developer can use the information redirect users from certain countries to regional websites or pages, or a system administrator can use the IP address information to isolate users from different countries.

Tips for Securing SSH in Linux Box (Securing SSH Series)

Secured Shell or SSH is a great way to enable a secure login for your UNIX / Linux Box. However there are precaution that you should take in order to properly secure SSH daemon from being scanned or attacked by script kiddies or automated bots.

This week I’m going to write a series of article on securing SSH on Ubuntu Linux Box (VPS) and I’m going to link to this post from time to time.

  1. Disable Root login, enable SSH login for a handful of users only
  2. Install and configure Fail2Ban
  3. Limit access with Firewall Rules (limit by ip block, or ip address)
  4. Limit connection rate to SSH port
  5. Disable keyboard interactive login, Use public-key login
  6. Security Security through obscurity: Hiding SSH version
  7. Security Security through obscurity: Change default SSH ports

Hope this will help in securing your Linux Box / Linux VPS

Ubuntu: How to create a lot of entropy for GPG key generation from command line

Desktop Ubuntu users may have several ways to generate entropy relatively secure GPG keys (=>2048 bits), usually by moving the mouse and by typing random words. However this creates certain problem, for command-line user (especially those who are connecting through remote VPS connection).

Here’s a tip on how to produce enough entropy for GPG key generation:

  • apt-get install rng-tools
  • rngd -r /dev/urandom
  • then, proceed to generate GPG keys as usual: gpg –gen-key

Hopefully this tips will help you get by generating GPS keys over those VPS connections!

Mypapit GNU/Linux blog is now served with CloudFlare!

After long and careful consideration, I decided to enable CloudFlare for my blog.

CloudFlare is a content delivery network which aims to enhance website security and performance. CloudFlare CDN offers protection againts many forms of malicious activity including: spammers, email harvesters, SQL Injection, XSS, denial-of-service attack and suspicious web requests. Therefore saving valueable bandwidth from the web hosting machine.

My Personal Experience with CloudFlare
After a while using CloudFlare, I’ve notice that:

  • My site uses less bandwidth
  • The php-fcgi uses less (valueable RAM)
  • Less comment spam received from blogs
  • Site loads faster, not prone to being bogged down during peak hour

So far, so good, I love using CloudFlare…

How to secure server from SYN-flood attack using iptables

SYN-flood attack is commonly utilized as a mean to disrupt network communication and it is a form of (Distributed Denial-of-Service) DDOS attack. RFC4987 details common mitigation to deal with SYN-flood attack.

However in this post, I’m going to share you the method that I use to reduce the risk of SYN-flood attack from my department computers, with iptables
[bash]
/sbin/iptables -N syn-flood
/sbin/iptables -A syn-flood -m limit –limit 100/second –limit-burst 100 -j RETURN
/sbin/iptables -A syn-flood -j LOG –log-prefix "SYN-flood attempt: "
/sbin/iptables -A syn-flood -j DROP
[/bash]

RFC4987 suggests the use of SYN-cookie for added protection. You can enable SYN-cookie protection in Linux by running this command (as root):
[bash]
echo 1 > /proc/sys/net/ipv4/tcp_syncookies
[/bash]

hope that helps…

Note: I’m not a full-time sysadmin as I’ve a different dayjob, but I was put incharged in securing part of my school’s computer network, so there.