Some services require you to generate random hex numbers to be used as a password or random auth token for authentication. The simplest method is to use this openssl cli command
openssl rand -hex 24
Free and Open Source blogger with an attitude
computer security related topic
Some services require you to generate random hex numbers to be used as a password or random auth token for authentication. The simplest method is to use this openssl cli command
openssl rand -hex 24The message sometimes appear when transferring files using scp.
In order to solve this, you need to edit “/etc/sshd_config” file and change or add this line:
UsePrivilegeSeparation yes
Then restart OpenSSH server. This will solve the kex protocol error problem,
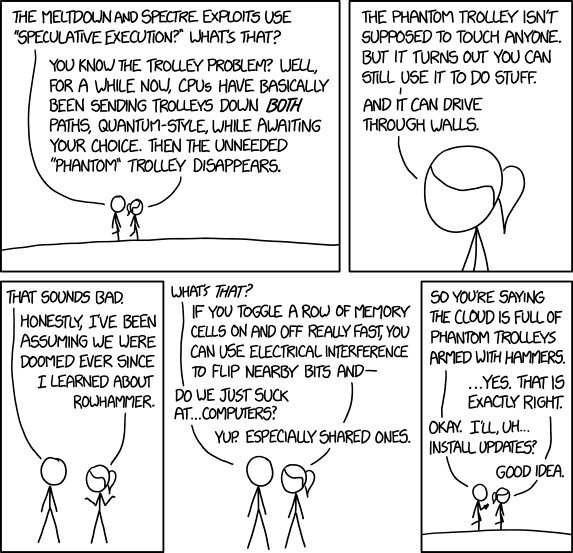
This XKCD strip explains what essentially Meltdown vulnerability which affects Intel microprocessor
Nmap (or Network Mapper) is probably the most popular network mapper around. However if you are running a very stable long-term support server, there are chances that your nmap database installation isn’t keep up to that.
Updating Nmap database
Nmap detection database consists of these files:
What you need to do is to download these files from Nmap Github project page and copy it to /usr/share/nmap/ folder.
Alternatively, you can use this script ‘nmap-update.sh’ which I’ve created based on this gist.
Copy all the files to /usr/share/nmap/ once all of them have been downloaded.
(y) (y)
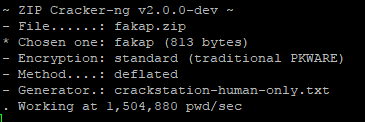
Cracking zip password can be made easy with cracker-ng
Installation is simple, assuming you use Debian, Ubuntu or any other similar operating system :
$ git clone https://github.com/BoboTiG/cracker-ng.git
$ cd cracker-ng

# For testers and contributors, always work with on the devel branch:
$ git checkout devel

$ make
Cracking is relatively simple, assuming you have downloaded the awesome Crackstation’s wordlist dictionary.
$ zipcracker-ng -f targetfile.zip -w crackstation-human-only.txt
Additionally zipcracker-ng can also be used with other brute-forcing cracking tool such as john and
$ john --incremental --stdout | zipcracker-ng -f FILE -

$ crunch 1 8 -f charset.lst lalpha | zipcracker-ng -f FILE -
Crackstation wordlist is one of the most (if not the most) comprehensive wordlist which can be used for the purpose of dictionary -attack on passwords.
The wordlist comes in two flavors:
Personally, I’ve already downloaded the full wordlist via torrent, and tested it against few PDF files (using pdfcrack) and UNIX password cracking (using John), all my test cases were successful. In my opinion, the wordlist is comprehensive for my need.
Since it looked like it took a significant effort to compile this wordlist, I rather advocate those who are interested to donate/buy the wordlist from: https://crackstation.net/buy-crackstation-wordlist-password-cracking-dictionary.htm