
Critical PHP Flaws: How to Update PHP 8.3, 8.4 and 8.5

Updated 22 October 2026. Commands below target Ubuntu/Debian package installations.

PHP has released emergency fixes for CVE-2026-109618 and CVE-2026-109619, both rated critical at CVSS 9.2. They can allow unauthenticated remote code execution. One involves unsafe out-of-memory cleanup; the other involves stale internal state across requests. Apache mod_php has a demonstrated attack before application code runs. PHP-FPM also requires patching. See the official announcement.

1. Check and update PHP

Back up your database, application files and configuration. Identify every runtime:

php -v
php --ini
dpkg -l 'php*' 'libapache2-mod-php*'

The CLI version may differ from the website. Check each virtual host, FPM pool, container and hosting panel.

Branch First fixed upstream version
PHP 8.3 8.3.36
PHP 8.4 8.4.27
PHP 8.5 8.5.12

Install these or later supported security releases. For PHP 8.3-FPM:

sudo apt update
apt-cache policy php8.3-common php8.3-fpm
sudo apt upgrade
sudo php-fpm8.3 -t
sudo systemctl restart php8.3-fpm

Substitute 8.4 or 8.5 for your installed branch. Review package upgrades, including extensions. If Apache uses mod_php:

sudo apache2ctl configtest
sudo systemctl restart apache2

Check vendor backports. Ubuntu fixes include 8.3.6-0ubuntu0.24.04.13 for 24.04 and 8.5.4-0ubuntu1.5 for 26.04. Compare complete revisions against Ubuntu’s security notice. Other repositories need their own advisories. An older-looking version can contain the fix.

Confirm the web runtime afterward and test login, uploads and database access. Updating WordPress or OJS alone does not update PHP.

2. Update containers separately

Host updates do not patch container PHP. Confirm a patched image exists, then replace app with your Compose service:

docker compose pull app
docker compose up -d --no-deps app
docker compose exec app php -v

Custom images require an updated base image and rebuild. Preserve persistent data. Shared-hosting users should request the exact patched revision.

3. Limit requests before PHP

In Nginx’s relevant server block:

client_max_body_size 8m;

Or inside the Apache virtual host:

LimitRequestBody 8388608

See the Nginx and Apache documentation. These impose an 8 MiB body limit. Adjust for legitimate uploads. In the active web runtime’s php.ini:

post_max_size = 8M
upload_max_filesize = 6M
max_file_uploads = 5
max_input_vars = 1000
max_input_nesting_level = 32
session.upload_progress.enabled = 0

Typical Ubuntu paths are /etc/php/8.3/fpm/php.ini for FPM and /etc/php/8.3/apache2/php.ini for mod_php. Adjust the branch number. php --ini reports CLI configuration only.

Test these example values. Disable file uploads if unused. Apply upload-progress settings at startup, then restart workers; application code and FPM .user.ini are too late for the confirmed early path.

Test Nginx with sudo nginx -t before reloading, or Apache with sudo apache2ctl configtest. These limits reduce exposure; they do not fix either CVE.

4. Emergency mitigation while patching

Prefer removing public PHP access and serving a static maintenance page. A PHP maintenance plugin still invokes PHP.

The OOM advisory recommends this incomplete emergency measure in the relevant FPM pool, such as /etc/php/8.3/fpm/pool.d/www.conf:

php_admin_value[memory_limit] = -1

This removes one controllable OOM trigger but permits unlimited per-request PHP memory, increasing denial-of-service risk. Use frontend limits and suitable cgroup/container boundaries. Underlying allocation failures remain dangerous; do not substitute RLIMIT_AS or RLIMIT_DATA. Audit overrides and restart all workers. Restore suitable finite PHP limits after patching.

For PHP 8.5, also set fatal_error_backtraces=0 in startup configuration. Remove invalid or obsolete per-request INI settings. These address specific stale-state paths only. Hiding warnings provides no protection.

5. Retire public PHP 7.4 applications

PHP 7.4 reached upstream end of life on 28 November 2022. Retire unused applications or migrate them to supported PHP. Legacy source patches and vendor fixes exist, but require explicit verification and should support temporary migration arrangements.

Remove forgotten subdomains, restrict administration through VPN/access policies, and keep FPM off public port 9000. Review logs, unexpected files, accounts and scheduled tasks. Patching does not remove existing backdoors. If compromise is suspected, isolate the system and preserve evidence. Follow NCSC guidance.
Neuropentracker: A Simple BitTorrent Tracker for Small Setups

I have published Neuropentracker, a simple BitTorrent tracker on GitHub:
https://github.com/mypapit/neuropentracker

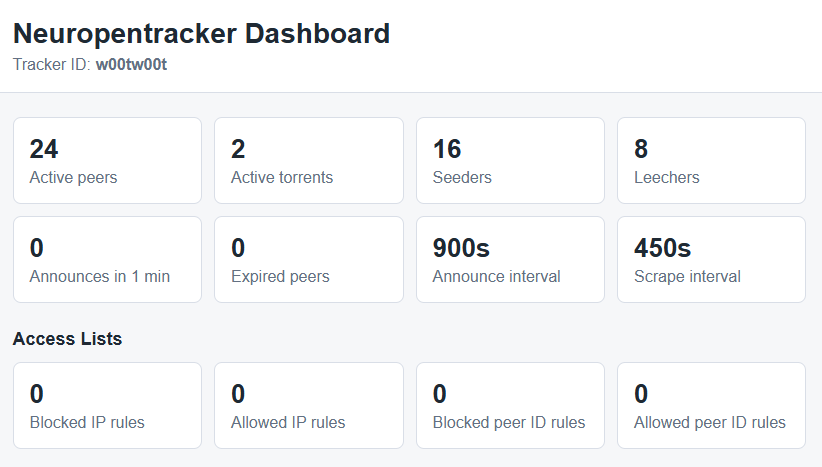
Dashboard Screenshot

What it is

Neuropentracker is written in PHP and is designed for small setups. It is suitable for small organizations, small communities, labs, schools, or internal file-sharing environments.

The main idea behind Neuropentracker is simplicity. It does not try to be a complete torrent portal or a large public tracker. It only provides the basic tracker functions needed by BitTorrent clients, such as announce and scrape support

It is designed for small organization to reduce server load when sharing large files. Instead of every user downloading from one central server,

What it is not

It is not intended for large public torrent sites. It does not include advanced features such as user accounts, ratio tracking, moderation system, or full torrent management portal. Administrators still need to secure the server, database, and tracker configuration properly.

Parting words

Overall, Neuropentracker is a lightweight and practical BitTorrent tracker for small and controlled environments. It is best used when the requirement is simple peer tracking, not a full torrent community platform.

How to convert Microsoft Office *.docx files to PDF using Linux in command-line

Here’s how to convert Microsoft Office *.docx files to PDF using Linux in Command Line.
This trick can also be used together with other documents files supported by LibreOffice

First make sure you’ve installed the latest version of LibreOffice for use in command line environment.
Assuming the user is ‘example’ and the filename to convert is ‘doc.pdf’.

libreoffice --headless -convert-to pdf --outdir /home/example/ /home/example/doc.docx

The conversion can also be adapted to PHP or Python using their respective shell_exec or subprocess directive.

This blog now runs on PHP 7!

Hi all,

I’m proud to announce to all the after several tinkering, this blog now runs on PHP 7 ! PHP 7 is the latest iteration of the popular general-purpose scripting language that is suited to web development.

PHP7 is touted to perform up to TWO TIMES faster than PHP5.

Here are the performance benchmark run by Kinsta has shown that PHP7 has significantly improved performance when compared to PHP 5.6.


  • WordPress 4.3.1 HHVM RepoAuthoritative benchmark result: 375.48 trans/sec
  • WordPress 4.3.1 HHVM benchmark result: 357.69 trans/sec
  • WordPress 4.3.1 PHP 7.0 benchmark result: 306.24 trans/sec
  • WordPress 4.3.1 PHP 5.6.16 benchmark result: 106.45 trans/sec

* Retrieved from Kinsta: The Definitive PHP 7.0 & HHVM Benchmark

Next I’ll update you with the guide on howto run and execute PHP7 and PHP5 side-by-side to cater for multiple websites.

Stay tuned, and expect more posts and updates from this venerable blog anyday now :p

How to convert between sqlite2 and sqlite3 database

Here’s a short guide on how to convert between sqlite2 to sqlite3 database file:

sqlite2 /path/to/mysqlite2.db .dump > backupfile
sqlite3 /path/to/mynewsqlite3.db < backupfile

Using the same method, you can convert sqlite3 db to sqlite2 db too!

p/s: Why you need to convert? because embedded device (read: iPhone and Android) only supports sqlite3 database, while PHP 5 by default supports sqlite2 database.

Thus, this method provide a convenient way to convert between the two different version of sqlite db format.

Recommended Reading

Securing Ajax and Web Services

It is undeniable that Web services and AJAX-ified interfaces are the trend now. Application that utilizes internet to retrieve data (such as mobile application or other thin client) uses web services alongside with its data format. AJAX-ified interface and website gives a modern and edgy look can make websites more attractive and can create great impression to the users.

However the issue of the web application security would still remain the same, if not more challenging, since there are so many ways to exploit the vulnerability of websites that utilizes Web Services and AJAX transfers on the background.

Therefore, it is imperative to use the right technique in order to evaluate the security of these services before deploying them out in the open.

For that matter, now I’m currently reading Ajax Security (Hoffman,B. & Sullivan, B.) and Securing Ajax applications (Wells, C.) which in my opinion is a pretty good start for somebody like me to understand common methods for securing web services and websites which uses AJAX heavily.

Hopefully the situation would improved as there are a lot of campaigns around to raise the state of awareness of web application security.